気に入った記事をブックマーク

- 気に入った記事を保存できます
保存した記事の一覧は、はてなブックマークで確認・編集ができます
- 記事を読んだ感想やメモを書き残せます
- 非公開でブックマークすることもできます
 medium.com/@renwa
エントリーの編集

エントリーの編集は全ユーザーに共通の機能です。
必ずガイドラインを一読の上ご利用ください。
 0

記事へのコメント0件
- 注目コメント
- 新着コメント
新着コメントはまだありません。
このエントリーにコメントしてみましょう。
このエントリーにコメントしてみましょう。
注目コメント算出アルゴリズムの一部にLINEヤフー株式会社の「建設的コメント順位付けモデルAPI」を使用しています
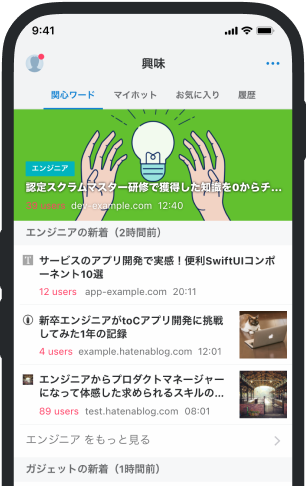
いまの話題をアプリでチェック!
- バナー広告なし
- ミュート機能あり
- ダークモード搭載
関連記事
Bypass SameSite Cookies Default to Lax and get CSRF
SameSite cookies, source:web.devSameSite Cookies the new cookie attribute that everyone is talkin... SameSite cookies, source:web.devSameSite Cookies the new cookie attribute that everyone is talking about, it can be used to prevent SOP bypasses and CSRF attacks. but first let's look what is it actually. SameSite is a cookie attribute which you can tell the browser to when it should send the specific cookie in a cross origin request, it has 3 types: SameSite None Will be sent in all cross origin
ブックマークしたユーザー


すべてのユーザーの
詳細を表示します
詳細を表示します
 gendai.media
 posfie.com
 huyukiitoichi.hatenadiary.jp
 www.businessinsider.jp
 forest.watch.impress.co.jp
 www.itmedia.co.jp
 qiita.com
 gigazine.net
 piyolog.hatenadiary.jp
 news.yahoo.co.jp
 blog.shibayu36.org
 summary.fc2.com
 www.newyorker.com
 markezine.jp
 www.nikkei.com
 levtech.jp
 suumo.jp
 levtech.jp
 levtech.jp